Researchers at Bitdefender have found an Android vulnerability, called GhostMap, that can crash your phone. Fortunately, this security hole hasn't been exploited yet, but on the other hand, Google hasn't patched it either.
What is GhostMap?
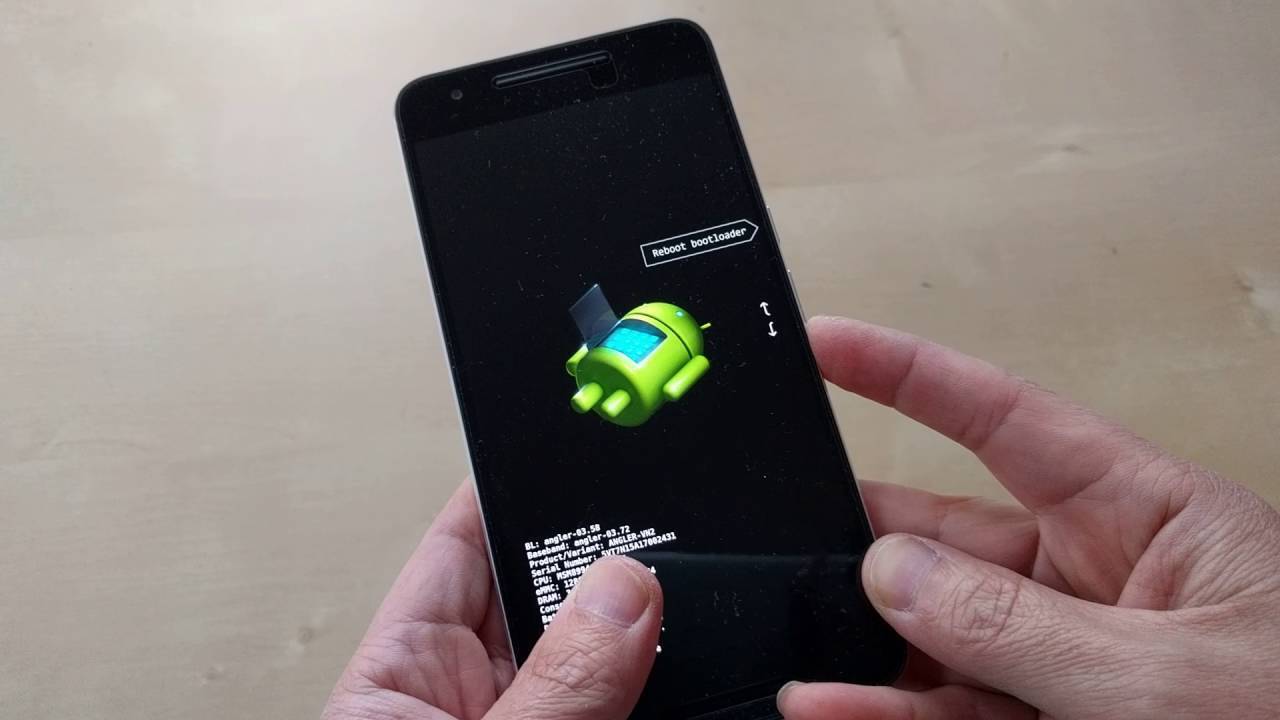
Bitdefender Labs researchers found that installing a specially crafted app can leave an Android phone stuck in a crash loop. | Image by Bitdefender
Investigation into this vulnerability began way back in August, when a malicious banking app crashed Bitdefender's emulators.
Security companies use these to test dangerous apps and services in a safe environment. The interesting thing was that the problem wasn't in the malicious app, but in Android itself. The operating system couldn't handle specific information about the compression that the ZIP files inside the app had.
This led to Bitdefender's emulators crashing and staying locked in a boot loop, where a normal smartphone would just cycle through restarting and crashing infinitely. The researchers dubbed this bug GhostMap, and one of the scary parts is that it can be baked into any app.
Any app could potentially exploit this
Malicious parties could potentially bake this exploit into innocent-looking apps and crash your phone. | Image by iMyFone
The big problem here is that normally, malicious apps require certain permissions to execute code and do harm, while the GhostMap vulnerability could be baked into any app, no permissions needed.
All hackers need to do is create an app that contains some of the problematic compression, and this app could brick your phone in seconds. The Android system tries to read the files and fails, crashes, then reboots, and the process is repeated in a loop.
Recommended For You
It crashes, Android restarts it, and on restart the service goes through the installed apps again, reads the same file again, and crashes again. The phone never finishes starting. This is the crash loop: system_server dies and restarts every few seconds, with no app ever opened and nothing on screen to say which app is responsible
- Alecsandru Cătălin DAJ, Bitdefender, November 05, 2026
There are no messages on the screen, no hints as to what the culprit might be, nothing. The guys at Bitdefender also developed a proof-of-concept app to show the vulnerability in action. And another scary detail is that you don't even need to open the app — the Android system crashes when it tries to read it after installation.
Poll
27 Votes
How do you handle the danger of Android exploits?
There's no fix (yet)
Bitdefender reported the vulnerability to Google, but the company closed the report with the status Won’t Fix (Not Reproducible), meaning Google's security team wasn't able to reproduce the bug.
The guys at Bitdefender then sent a second report which included the working proof-of-concept app, only to get another denial. Google replied that the issue was "outside the scope of a security update fix." This label means that the proposed work does not belong in a security patch because it doesn't directly solve a security vulnerability.
To put it simply, Bitdefender didn't provide a fix to the issue, so Google engineers have to do the heavy lifting and fix the Android exploit themselves.
The bug was then reportedly passed to "the relevant team for review," but the result of all this back-and-forth is that there's still no fix for this vulnerability. However, you reading this news publicly changes the game for Google completely.
The cat's out of the bag now
The exploit is now public, which means a fix might be coming sooner rather than later. | Image by Bleeping Computer
Bitdefender has now disclosed the vulnerability publicly, meaning not only you and I now know about it, but most hackers out there do too.
This changes the game for everybody, including Google, as malicious parties will most likely start to bake this exploit into innocent-looking apps and try to push them to the Play Store.
On the other hand, making the exploit public puts some pressure on "the relevant team" working on the issue at Google, and potentially accelerates the upcoming fix. Meanwhile, stay away from suspicious apps from unknown or shady sources.
Read more about Android vulnerabilities and security issues here:
Get a free Galaxy A17 with Straight Talk. To claim this deal, you need to pair the phone with activation on a Silver Unlimited Plan or higher. This tier costs $45 per month. Offer valid through 01/10/27 while supplies last online.
Mariyan, a tech enthusiast with a background in Nuclear Physics and Journalism, brings a unique perspective to PhoneArena. His childhood curiosity for gadgets evolved into a professional passion for technology, leading him to the role of Editor-in-Chief at PCWorld Bulgaria before joining PhoneArena. Mariyan's interests range from mainstream Android and iPhone debates to fringe technologies like graphene batteries and nanotechnology. Off-duty, he enjoys playing his electric guitar, practicing Japanese, and revisiting his love for video games and Haruki Murakami's works.
A discussion is a place, where people can voice their opinion, no matter if it
is positive, neutral or negative. However, when posting, one must stay true to the topic, and not just share some
random thoughts, which are not directly related to the matter.
Things that are NOT allowed:
Off-topic talk - you must stick to the subject of discussion
Offensive, hate speech - if you want to say something, say it politely
Spam/Advertisements - these posts are deleted
Multiple accounts - one person can have only one account
Impersonations and offensive nicknames - these accounts get banned
To help keep our community safe and free from spam, we apply temporary limits to newly created accounts:
New accounts created within the last 24 hours may experience restrictions on how frequently they can
post or comment.
These limits are in place as a precaution and will automatically lift.
Moderation is done by humans. We try to be as objective as possible and moderate with zero bias. If you think a
post should be moderated - please, report it.
Have a question about the rules or why you have been moderated/limited/banned? Please,
contact us.

Things that are NOT allowed:
To help keep our community safe and free from spam, we apply temporary limits to newly created accounts: