According to a new report, hackers, whom researchers believe with a high degree of confidence are connected to part of Russia’s Foreign Intelligence Service, tried to exploit iOS and Android vulnerabilities that had already been patched.
The plan was to trick a target into visiting a compromised website
Their goal was to hack visitors to infected websites, including one that celebrated the 250 years that had passed since the Declaration of Independence had been signed. Other websites that were created and then targeted included some that were linked to Russia's ongoing war against Ukraine.
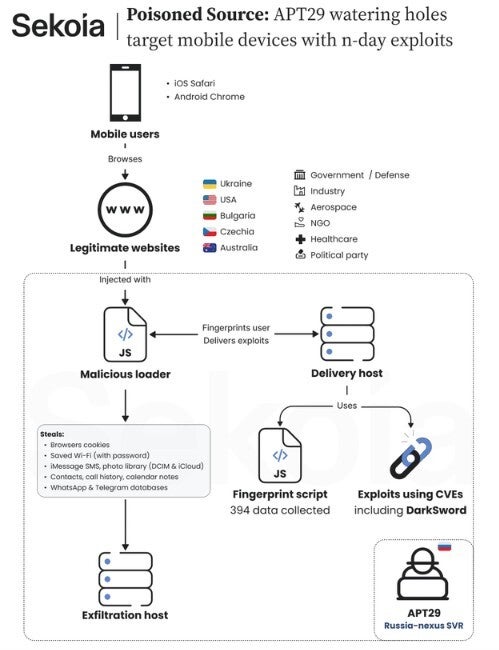
When a large number of iOS or Android users visited a site, the hackers would use JavaScript to profile the devices. Attacks attempted to steal browser cookies, Wi-Fi passwords, and mobile device data.
One of the impersonated websites was the aforementioned america250.org, which was created by business executives and a group of non-partisan politicians. This is what the hackers did.
A flowchart shows how the n-day attack works. | Image by Sekoia
They registered the america250[.]holiday web address to trick those looking for the real america250.org site. The hackers set it up so that the bogus website showed content from the real site and added malicious JavaScript.
How an attack takes place
Researchers working for security firm Sekoia said that the attackers chose the anniversary website because it was associated with a "high-profile national celebration" and conducted invitation-themed spear-phishing campaigns.
Recommended For You
Such an attack involves using fake calendar invites, event notifications, and other bogus ways to get a targeted individual or a specific organization to visit the fake website where their phone can be compromised and mobile data stolen.
Another example involved the creation of a website with the address theowo[.]club, which was a proxy for the legitimate site Raffles of London OWO. This is a luxury hotel in London that happens to be near some important UK locations such as the Ministry of Defence and 10 Downing Street, where the Prime Minister works and lives.
Supposedly, Ukrainian President Volodymyr Zelenskyy stayed at the hotel on October 14.
During the first stage of an attack, JavaScript was used to profile the target's browser and device. That information was used by the attackers to deliver one of three zero-click exploit chains. Zero-click means they work without needing any interaction from the target.
Why the threat of an "n-day" attack should make you always update your phone's OS in a timely manner
All of the vulnerabilities were "n-day" attacks. That means that any flaw had already been patched. Wouldn't that seem like a waste of time to attack if all of the vulnerabilities were patched? No, because the attacks will still work if a target's device is running an outdated version of iOS or Android.
Poll
0 Votes
Do you worry about attacks like this?
Let this be a warning to you that you should always make sure that your phone is updated to the latest version of iOS or Android.
Get a free Galaxy A17 with Straight Talk. To claim this deal, you need to pair the phone with activation on a Silver Unlimited Plan or higher. This tier costs $45 per month. Offer valid through 01/10/27 while supplies last online.
Alan, an ardent smartphone enthusiast and a veteran writer at PhoneArena since 2009, has witnessed and chronicled the transformative years of mobile technology. Owning iconic phones from the original iPhone to the iPhone 15 Pro Max, he has seen smartphones evolve into a global phenomenon. Beyond smartphones, Alan has covered the emergence of tablets, smartwatches, and smart speakers.
A discussion is a place, where people can voice their opinion, no matter if it
is positive, neutral or negative. However, when posting, one must stay true to the topic, and not just share some
random thoughts, which are not directly related to the matter.
Things that are NOT allowed:
Off-topic talk - you must stick to the subject of discussion
Offensive, hate speech - if you want to say something, say it politely
Spam/Advertisements - these posts are deleted
Multiple accounts - one person can have only one account
Impersonations and offensive nicknames - these accounts get banned
To help keep our community safe and free from spam, we apply temporary limits to newly created accounts:
New accounts created within the last 24 hours may experience restrictions on how frequently they can
post or comment.
These limits are in place as a precaution and will automatically lift.
Moderation is done by humans. We try to be as objective as possible and moderate with zero bias. If you think a
post should be moderated - please, report it.
Have a question about the rules or why you have been moderated/limited/banned? Please,
contact us.

Things that are NOT allowed:
To help keep our community safe and free from spam, we apply temporary limits to newly created accounts: