Malware installs phony Google App Store on your device
Earlier this week, Apple's senior vice president of worldwide marketing, Phil Schiller, tweeted out a report showing that 99% of malware is targeted at Android devices. One sneaky way to inject this poison into the veins of your Android device was disclosed by Symantec. When you sync your Android flavored device to a Windows PC, this malware, named Trojan.Droidpak, creates a phony version of the Google Play Store while the device is in USB debugging mode. This is a mode normally used by developers, but is sometimes used when rooting an Android device.
Symantec has made an interesting discovery, This particular malware, when installed on an Android device, looks for Korean on-line banking apps, deletes them, and installs an infected version of the app. But there are solutions to avoid getting infected. Symantec suggests that Android users turn off USB debugging when not in use. Symantec also suggests that Android users be very cautious when syncing to an unknown PC, and install security software like Norton Mobile Security.
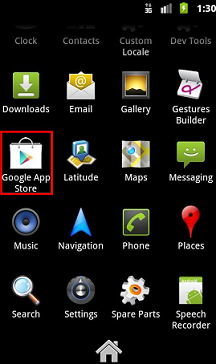
We have a screen shot from an infected Android handset for you to take a gander at, and most of you right away will note how the malicious app is listed as Google APP Store. If something doesn't look kosher on your app tray, odds are that you should tread lightly.
"The malicious APK actually looks for certain Korean online banking applications on the compromised device and, if found, prompts users to delete them and install malicious versions. It also intercepts SMS messages received by the user and sends them a remote server."-Flora Liu, Symantec researcher
source:
Symantec,
PCWorld via
BGR
Read the latest from Alan Friedman


Things that are NOT allowed:
To help keep our community safe and free from spam, we apply temporary limits to newly created accounts: